Microsegmentation implementation

Microsegmentation implementation 
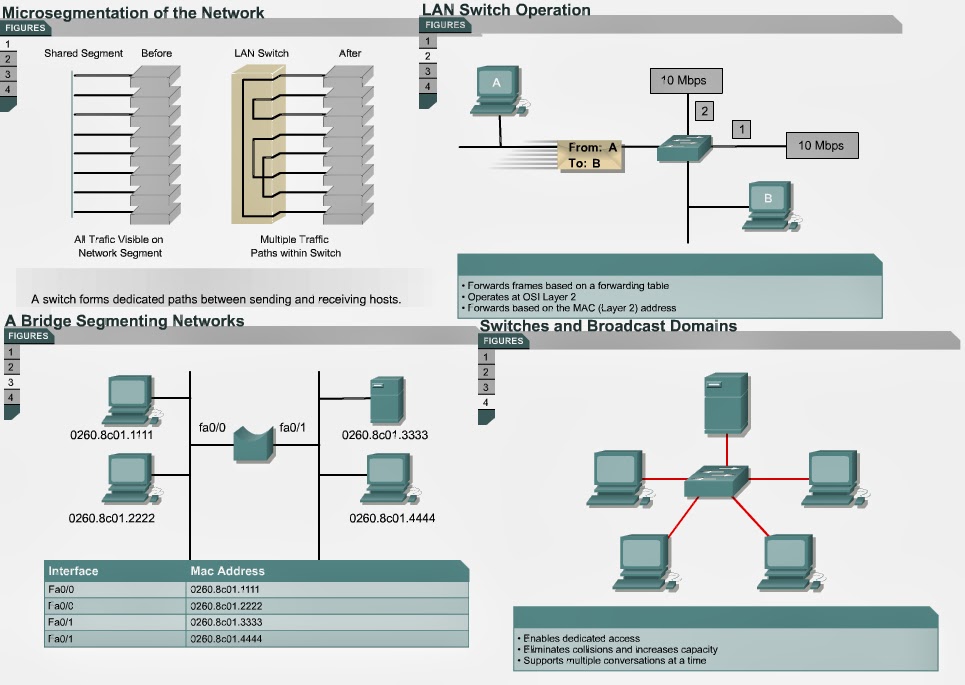
4.3.6 This page will explain the functions of a switch in a LAN due to microsegmentation.
LAN switches are considered multi-port bridges with no collision domain, because of microsegmentation. Data is exchanged at high speeds by switching the frame to its destination. By reading the destination MAC address Layer 2 information, switches can achieve high-speed data transfers, much like a bridge does. This process leads to low latency levels and a high rate of speed for frame forwarding.  
Ethernet switching increases the bandwidth available on a network. It does this by creating dedicated network segments, or point-to-point connections, and connecting these segments in a virtual network within the switch. This virtual network circuit exists only when two nodes need to communicate. This is called a virtual circuit because it exists only when needed, and is established within the switch.
Even though the LAN switch reduces the size of collision domains, all hosts connected to the switch are still in the same broadcast domain. Therefore, a broadcast from one node will still be seen by all the other nodes connected through the LAN switch.
Switches are data link layer devices that, like bridges, enable multiple physical LAN segments to be interconnected into a single larger network. Similar to bridges, switches forward and flood traffic based on MAC addresses. Because switching is performed in hardware instead of in software, it is significantly faster. Each switch port can be considered a micro-bridge acting as a separate bridge and gives the full bandwidth of the medium to each host.
The next page will discuss collisions.

Comments

Popular posts from this blog

Windowing

Windowing 11.1.5 This page will explain how windows are used to transmit data. Data packets must be delivered to the recipient in the same order in which they were transmitted to have a reliable, connection-oriented data transfer. The protocol fails if any data packets are lost, damaged, duplicated, or received in a different order. An easy solution is to have a recipient acknowledge the receipt of each packet before the next packet is sent. If a sender had to wait for an ACK after each packet was sent, throughput would be low. Therefore, most connection-oriented, reliable protocols allow multiple packets to be sent before an ACK is received. The time interval after the sender transmits a data packet and before the sender processes any ACKs is used to transmit more data. The number of data packets the sender can transmit before it receives an ACK is known as the window size, or window. TCP uses expectational ACKs. This means that the ACK number refers to the next packet that is...

OSI layers / Peer-to-peer communications / TCP/IP model

OSI layers 2.3.4 This page discusses the seven layers of the OSI model. The OSI reference model is a framework that is used to understand how information travels throughout a network. The OSI reference model explains how packets travel through the various layers to another device on a network, even if the sender and destination have different types of network media. In the OSI reference model, there are seven numbered layers, each of which illustrates a particular network function. - Dividing the network into seven layers provides the following advantages: • It breaks network communication into smaller, more manageable parts. • It standardizes network components to allow multiple vendor development and support. • It allows different types of network hardware and software to communicate with each other. • It prevents changes in one layer from affecting other layers. • It divides network communication into smaller parts to make learning it easier to understand. In the foll...

1.2.2 RIP V2 Features

 1.2.2 RIP V2 Features This page will discuss RIP v2, which is an improved version of RIP v1. Both versions of RIP share the following features: It is a distance vector protocol that uses a hop count metric. It uses hold down timers to prevent routing loops – default is 180 seconds. It uses split horizon to prevent routing loops. It uses 16 hops as a metric for infinite distance. RIP v2 provides prefix routing, which allows it to send out subnet mask information with the route update. Therefore, RIP v2 supports the use of classless routing in which different subnets within the same network can use different subnet masks, as in VLSM. RIP v2 provides for authentication in its updates. A set of keys can be used on an interface as an authentication check. RIP v2 allows for a choice of the type of authentication to be used in RIP v2 packets. The choice can be either clear text or Message-Digest 5 (MD5) encryption. Clear text is the default. MD5 can be used t...