Shortest path algorithm

Shortest path algorithm
2.2.4 This page will explain how OSPF uses the shortest-path algorithm to determine the best path to a destination.
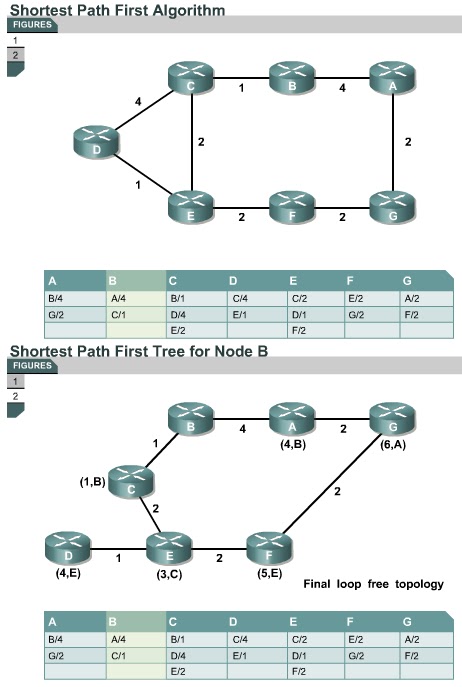
In this algorithm, the best path is the lowest cost path. Edsger Wybe Dijkstra, a Dutch computer scientist, formulated the shortest path-algorithm, also known as Dijkstra's algorithm. The algorithm considers a network to be a set of nodes connected by point-to-point links. Each link has a cost. Each node has a name. Each node has a complete database of all the links and so complete information about the physical topology is known. All router link-state databases, within a given area, are identical. The table in Figure shows the information that node D has received. For example, D received information that it was connected to node C with a link cost of 4 and to node E with a link cost of 1.
The shortest path algorithm then calculates a loop-free topology using the node as the starting point and examining in turn information it has about adjacent nodes. In Figure , node B has calculated the best path to D. The best path to D is by way of node E, which has a cost of 4. This information is converted to a route entry in B which will forward traffic to C. Packets to D from B will flow B to C to E, then to D in this OSPF network.
In the example, node B determined that to get to node F the shortest path has a cost of 5, through node C. All other possible topologies will either have loops or a higher cost paths.
The next page will explain the concept of OSPF networks.

Comments

Popular posts from this blog

Windowing

Windowing 11.1.5 This page will explain how windows are used to transmit data. Data packets must be delivered to the recipient in the same order in which they were transmitted to have a reliable, connection-oriented data transfer. The protocol fails if any data packets are lost, damaged, duplicated, or received in a different order. An easy solution is to have a recipient acknowledge the receipt of each packet before the next packet is sent. If a sender had to wait for an ACK after each packet was sent, throughput would be low. Therefore, most connection-oriented, reliable protocols allow multiple packets to be sent before an ACK is received. The time interval after the sender transmits a data packet and before the sender processes any ACKs is used to transmit more data. The number of data packets the sender can transmit before it receives an ACK is known as the window size, or window. TCP uses expectational ACKs. This means that the ACK number refers to the next packet that is...

OSI layers / Peer-to-peer communications / TCP/IP model

OSI layers 2.3.4 This page discusses the seven layers of the OSI model. The OSI reference model is a framework that is used to understand how information travels throughout a network. The OSI reference model explains how packets travel through the various layers to another device on a network, even if the sender and destination have different types of network media. In the OSI reference model, there are seven numbered layers, each of which illustrates a particular network function. - Dividing the network into seven layers provides the following advantages: • It breaks network communication into smaller, more manageable parts. • It standardizes network components to allow multiple vendor development and support. • It allows different types of network hardware and software to communicate with each other. • It prevents changes in one layer from affecting other layers. • It divides network communication into smaller parts to make learning it easier to understand. In the foll...

1.2.2 RIP V2 Features

 1.2.2 RIP V2 Features This page will discuss RIP v2, which is an improved version of RIP v1. Both versions of RIP share the following features: It is a distance vector protocol that uses a hop count metric. It uses hold down timers to prevent routing loops – default is 180 seconds. It uses split horizon to prevent routing loops. It uses 16 hops as a metric for infinite distance. RIP v2 provides prefix routing, which allows it to send out subnet mask information with the route update. Therefore, RIP v2 supports the use of classless routing in which different subnets within the same network can use different subnet masks, as in VLSM. RIP v2 provides for authentication in its updates. A set of keys can be used on an interface as an authentication check. RIP v2 allows for a choice of the type of authentication to be used in RIP v2 packets. The choice can be either clear text or Message-Digest 5 (MD5) encryption. Clear text is the default. MD5 can be used t...